Prove that what you shipped is exactly what your team built

Prove that what you shipped is exactly what your team built

Prove that what you shipped is exactly what your team built

SignPath gives security and engineering leaders cryptographic proof that every release you’re accountable for is authentic, unmodified, and approved at every step by the right people. When an auditor asks, a customer demands evidence, or an incident happens, you can show exactly what shipped, how it was approved, and where it came from.

TRUSTED BY GLOBAL LEADERS

What’s going wrong today

Code signing alone isn’t proof

Today, a signature ensures a file hasn’t changed since it was signed. It doesn’t prove that the software is trustworthy, or that it was properly built and released. If an insider, a compromised dependency, or any tool or person with development access can modify your software between before release, you won’t know until the damage is done.

Today, a signature ensures a file hasn’t changed since it was signed. It doesn’t prove that the software is trustworthy, or that it was properly built and released. If an insider, a compromised dependency, or any tool or person with development access can modify your software between before release, you won’t know until the damage is done.

Developers need to move fast – but lack secure, scalable tools

Developers need to move fast –
but lack secure, scalable tools

Local scripts, token-based signing, and inconsistent key handling waste time and create risk. Code signing is treated as a bottleneck, not a security feature.

Security teams can’t enforce signing policies or control signing events

Even well-configured CI/CD pipelines can be silently compromised through configuration drift, caching, skipping approvals or keys simply stored as secrets in build tools.

91%

of all organizations faced a Software Supply Chain Attack*

*Enterprise Strategy Group (TechTarget), The Growing Complexity of Securing the Software Supply Chain, 2024 – survey of 350+ organizations.

When nearly everyone’s been hit, trusting your pipeline isn’t a strategy – releasing with proof is.

Keeping CI/CD pipelines secure is harder than ever

Without visibility into what gets signed and when, policy enforcement becomes a matter of trust. And trust without control is fragile.

91%

of all organizations faced a Software Supply Chain Attack*

*Enterprise Strategy Group (TechTarget), The Growing Complexity of Securing the Software Supply Chain, 2024 – survey of 350+ organizations.

When nearly everyone’s been hit, trusting your pipeline isn’t a strategy – releasing with proof is.

Protect the whole process. Not just the signature.

SignPath verifies where your code came from, enforces your development and release policies automatically, and signs and proves every release – in one integrated platform built for security, audits, compliance, and incident preparedness.

SignPath verifies where your code came from, enforces your development and release policies automatically, and signs and proves every release – in one integrated platform built for security, audits, compliance, and incident preparedness.

1

Policy enforcement, not paperwork

Lock down conditions for signing events: what can be signed, and under what conditions – enforced automatically, not checked manually.

2

Full pipeline verification, not just signing

Most tools protect keys or sign files; SignPath verifies source origin, build pipeline, and artifact content, and produces a provenance record.

3

Built for the regulation you already deal with

Verifiable evidence is generated automatically alongside the signed release – covering the frameworks (EU CRA, NIST SSDF, IEC 62443) buyers are already being asked about.

SignPath Software Integrity Platform
Three systems. One unbroken chain of proof.

Three integrated components make up the SignPath Software Integrity Platform.

Integrity

Enforcement

Proof

Control your software production process with policies

Define and verify policies for

• Source control and reviews

• Security and Testing

• Build and artifact integrity

Zero-trust verification on the control plane

Deliver your releases with signatures that
devices and platforms can enforce

• Content policies and declarative signing

• Key and certificate management

• Secure key management and crypto agility

• Easy integration

• Signing and re-signing full releases

• Enforcement through target platform

• Content policies and declarative signing

• Key and certificate management

• Secure key management and
crypto agility

• Easy integration

• Signing and re-signing full
releases

• Enforcement through target
platform

Prove what you shipped with verifiable attestations

• Cloud-based development: attestations by SignPath

• On-premises: self- or 3rd party attestations

• SLSA and in-toto attestations

• Signed SBOMs

Nothing ships on trust alone.

HOW IT WORKS

HOW IT WORKS

Every release is verified before it’s signed.

Most tools sign whatever they’re handed. SignPath verifies first – where the release came from, who approved it, and what’s inside – read directly from your CI/CD and source control, so it can’t be forged. Only a build that passes gets signed, and every release ships with proof you can show on demand.
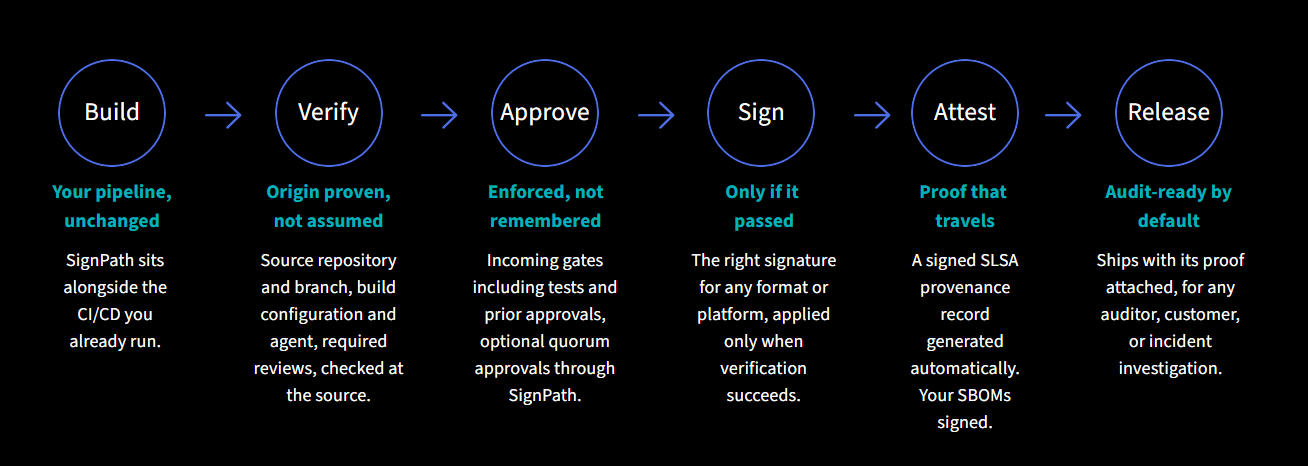
Build

Your pipeline, unchanged

Your pipeline, unchanged

SignPath sits alongside the CI/CD you already run.

SignPath sits alongside the CI/CD you already run.

Verify

Origin proven, not assumed

Origin proven, not assumed

Source repository and branch, build configuration and agent, required reviews, checked at the source.

Source repository and branch, build configuration and agent, required reviews, checked at the source.

Approve

Enforced, not remembered

Enforced, not remembered

Incoming gates including tests and prior approvals, optional quorum approvals through SignPath.

Incoming gates including tests and prior approvals, optional quorum approvals through SignPath.

Sign

Only if it
passed

Only if it passed

The right signature for any format or platform, applied only when verification succeeds.

The right signature for any format or platform, applied only when verification succeeds.

Attest

Proof that
travels

Proof that travels

A signed SLSA provenance record generated automatically. Your SBOMs signed.

A signed SLSA provenance record generated automatically. Your SBOMs signed.

Release

Audit-ready by default

Audit-ready by default

Ships with its proof attached, for any auditor, customer, or incident investigation.

Ships with its proof attached, for any auditor, customer, or incident investigation.

Build

Your pipeline, unchanged

SignPath sits alongside the CI/CD you already run.

Verify

Origin proven, not assumed

Source repository and branch, build configuration and agent, required reviews, checked at the source.

Approve

Enforced, not remembered

Incoming gates including tests and prior approvals, optional quorum approvals through SignPath.

Sign

Only if it
passed

The right signature for any format or platform, applied only when verification succeeds.

Attest

Proof that
travels

A signed SLSA provenance record generated automatically. Your SBOMs signed.

Release

Audit-ready by default

Ships with its proof attached, for any auditor, customer, or incident investigation.

Verified at the source

SignPath verifies what it checks directly from your CI/CD and source-control systems, not from anything a development team controls. Origin, SSDLC practices, build integrity – policy input and records can’t be forged.

Fits the stack you run

Native integrations for GitHub, GitLab, Azure DevOps, Jenkins and TeamCity – or call SignPath from any platform via REST APIs or command line tools.

Live in about two hours

Wire up a new project in no time. Full separate of test and setup from production. Already signing code? Integrate your legacy tools and workflows, improve incrementally.

Each step feeds the next – one unbroken chain of proof, from source to production.

Each step feeds the next – one unbroken chain of proof, from source to production.

TESTIMONIALS

TESTIMONIALS

Security and Engineering leaders using SignPath

"SignPath protects modern software supply chains from source to release by verifying every step, enforcing development and build policies and only signing secure and legit release artifacts."

Alex Hamby

VP of Engineering, Tricentis GmbH

Prove it, every time.

Book a platform walkthrough with our team and see how SignPath turns your release process into verifiable proof – every build, every approval, every release.

End-to-end release integrity, without the complexity.
EU-hosted and data residency options available on request.

Prove it, every time.

Book a platform walkthrough with our team and see how SignPath turns your release process into verifiable proof – every build, every approval, every release.

End-to-end release integrity, without the complexity.
EU-hosted and data residency options available on request.

Security & Trust